The Real Cost of Shadow IT — And How Businesses Can Control It
With the rise of SaaS and AI tools, Shadow IT is growing rapidly. Businesses should focus on visibility, governance, employee awareness, access controls, and approved tool ecosystems rather than simply blocking everything. The goal is to enable innovation safely while maintaining control over business data and systems.
Effective Shadow IT management today is not just an IT issue — it is a business governance priority.
The Problem Most Businesses Don’t Realize They Already Have
A finance executive uploads company data into an AI tool to speed up reporting.
A sales team starts using a free CRM without informing IT.
An operations manager shares sensitive files using a personal cloud drive because “it’s easier.”
None of these decisions are made with bad intentions.
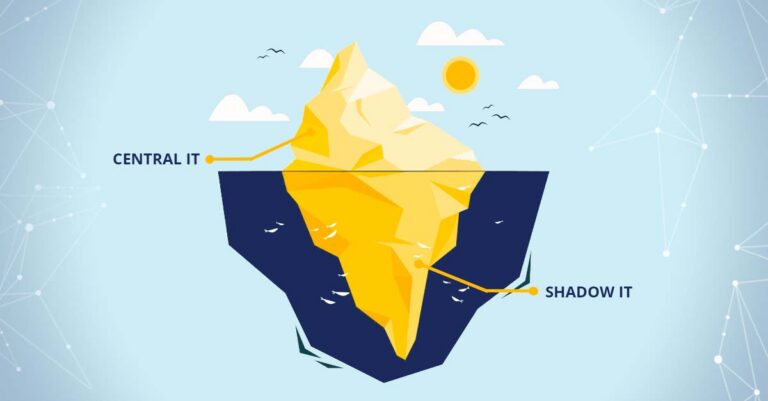
Yet collectively, they create one of the biggest modern business risks: Shadow IT.
For many MSMEs and growing businesses, Shadow IT often starts as a productivity shortcut. Teams want faster tools, simpler workflows, and less dependency on formal processes. But over time, these unofficial apps, systems, and cloud platforms create serious concerns around:
The reality is simple:
This guide breaks down practical ways businesses can identify, reduce, and manage Shadow IT risks without becoming overly restrictive.Businesses today are not struggling because employees use technology. They struggle because they lose visibility and control over it.
What Is Shadow IT?
Shadow IT refers to any software, application, device, cloud platform, or technology solution used within an organization without formal approval or oversight from the IT or governance function.Examples include:
In smaller businesses, Shadow IT often emerges because there is limited formal IT governance. Employees prioritize convenience and speed over security considerations.
Why Shadow IT is Growing Faster Than Ever
The rise of SaaS, low-code platforms, and AI tools has made technology adoption incredibly easy.Today, anyone can:
This accessibility is beneficial for innovation.
But it also creates a governance nightmare.
According to IBM’s Cost of a Data Breach Report, stolen or compromised credentials and cloud misconfigurations continue to be among the leading causes of breaches globally.
Similarly, Gartner has repeatedly highlighted that business-led technology adoption is increasing faster than centralized IT oversight in many organizations.
The problem becomes even more dangerous when:
Practical Ways to Mitigate Shadow IT Risks
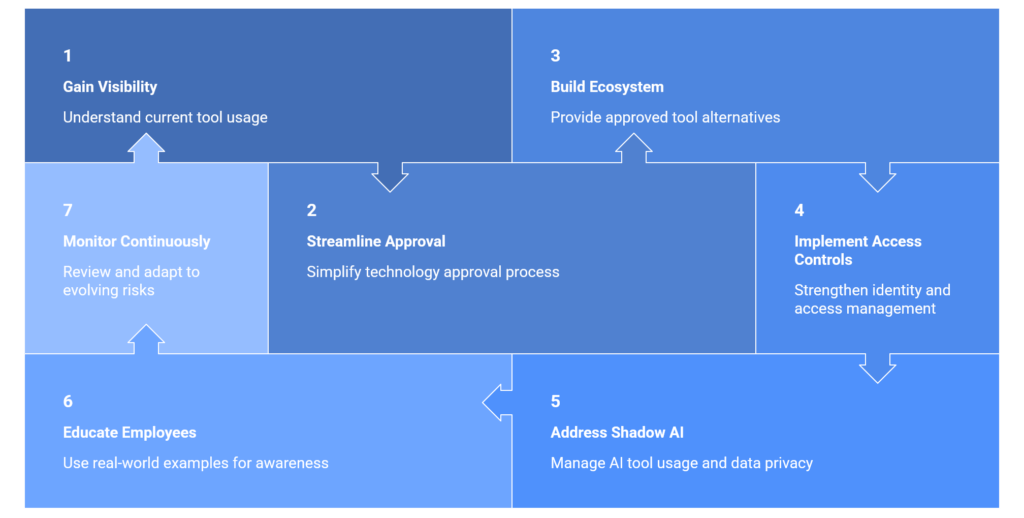
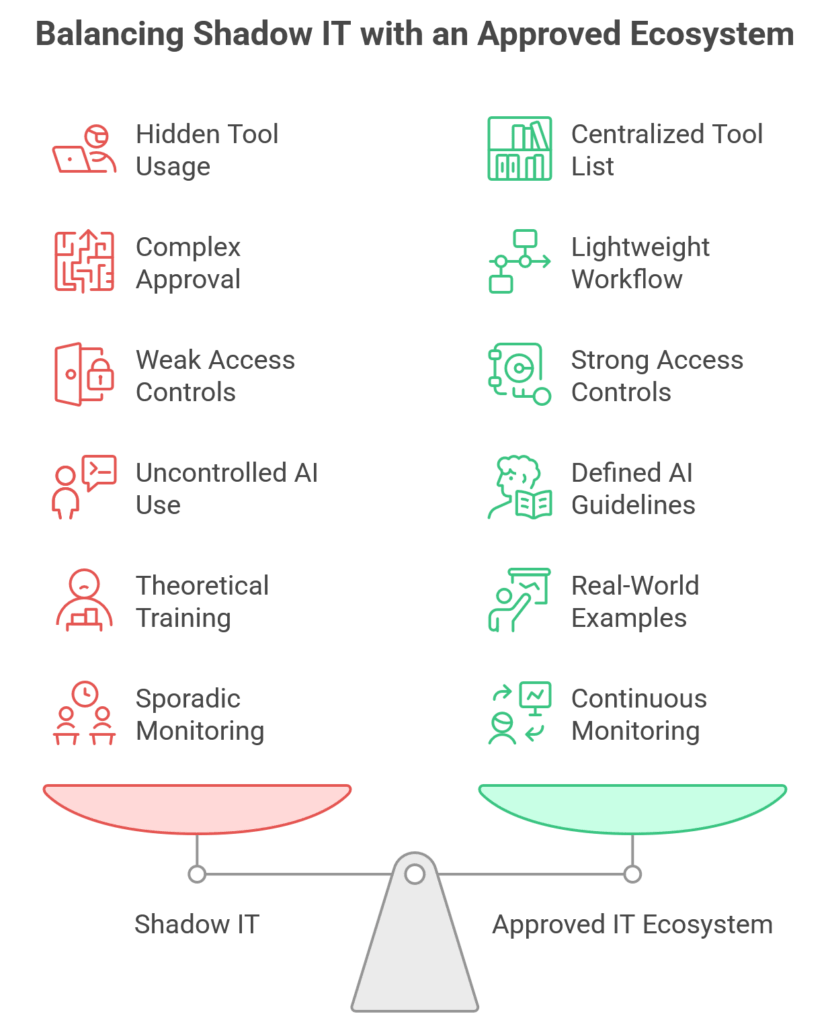
1. Start with Visibility, Not Punishment
You cannot secure what you cannot see.
The first step is understanding:
– What tools employees are using
– Which departments use them
– What data flows into them
– Whether integrations exist
Practical methods include:
– Reviewing browser extension usage
– SaaS discovery tools
– Firewall and DNS logs
– Expense audits for software subscriptions
– Employee surveys
– Access reviews
Many businesses are surprised to discover dozens — sometimes hundreds — of unofficial tools already in use.
2. Create a Simple Technology Approval Process
One major reason Shadow IT grows is because approval processes are painful.
Instead of complex bureaucracy:
– Create lightweight approval workflows
– Define risk-based categories
– Allow fast-track approvals for low-risk tools
The easier governance becomes, the lower the Shadow IT risk.
3. Build an “Approved Tools Ecosystem”
Employees seek convenience.
If businesses provide modern, efficient alternatives, unofficial tool usage reduces naturally.
Maintain a centralized list of:
– Approved SaaS applications
– AI tools
– Collaboration platforms
– Automation solutions
– File-sharing systems
This also improves:
Standardization
Supportability
Security monitoring
4. Implement Strong Access Controls
Identity and access management is one of the strongest defenses against Shadow IT risks.
Businesses should prioritize:
– Multi-factor authentication (MFA)
– Single Sign-On (SSO)
– Role-based access
– Periodic access reviews
– Removal of inactive accounts
Even if unofficial tools exist, stronger identity controls reduce damage potential.
5. Address Shadow AI Separately
Shadow AI deserves dedicated attention.
Employees increasingly use:
– AI chatbots
– AI summarization tools
– AI coding assistants
– AI analytics platforms
without understanding data privacy implications.
Organizations should define:
– What data can be shared with AI tools
– Which AI platforms are approved
– Whether AI training on company data is disabled
– AI usage guidelines for employees
This is rapidly becoming a major governance priority.
6. Educate Employees Through Real Examples
Cybersecurity awareness training often fails because it feels theoretical.
Instead:
– Use relatable business examples
– Demonstrate actual risks
– Show how breaches occur
– Explain consequences practically
For example:
– Uploading payroll data into public AI tools
– Sharing client files via personal drives
– Reusing passwords across SaaS platforms
Employees make better decisions when they understand business impact.
7. Monitor Continuously
Shadow IT management is not a one-time exercise.
Businesses should continuously review:
– New SaaS subscriptions
– Third-party integrations
– User access patterns
– Cloud usage trends
– AI adoption across departments
Risk landscapes evolve constantly.
Governance must evolve too.
Shadow IT Is Also a Leadership Problem
Many organizations treat Shadow IT purely as an IT issue. It is not. It is fundamentally a:If employees constantly bypass systems, leaders should ask:
Are existing tools ineffective? Are workflows too slow? Is innovation discouraged? Is governance disconnected from operational reality?
Strong governance should enable productivity — not block it.
Visibility
Governance
Education
Secure enablement
Practical controls
The businesses that succeed will be the ones that balance:
agility,
innovation,
and operational discipline.
Because in modern organizations, unmanaged technology quickly becomes unmanaged risk.