Controls & Audit
Controls, governance, operational trust, risk visibility, and how businesses slowly lose control.
Most businesses don’t fail because of one dramatic event.
They fail quietly:
– through ignored processes,
– invisible risks,
– undocumented workarounds,
– weak approvals,
– unmanaged access,
– operational shortcuts,
– and controls that exist only on paper.
This thread explores:
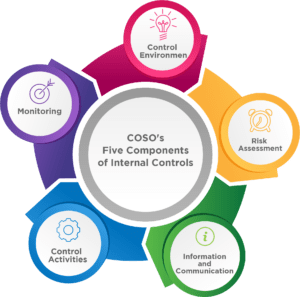
– internal controls,
– audits,
– governance,
– cybersecurity,
– ITGC,
– operational risk,
– process maturity,
– and the systems businesses rely on without realizing it.
Not from a purely compliance perspective.
But from the perspective of:
how businesses actually operate behind the scenes.
Because controls are not just audit requirements.
They are:
operational trust systems,
visibility mechanisms,
and foundations for scalable businesses.
What You’ll Find Here
What This Thread Tries To Achieve
This thread aims to:Connected Threads
Controls influence everything:🟥 Technology → because every tool and automation creates new risks
🟨 Business & Work → because operational behavior shapes control effectiveness
🟩 Money & Taxes → because financial trust depends on governance and process discipline
Eventually:
– weak controls become financial issues,
– operational shortcuts become audit findings,
– and unmanaged systems become business risks.
Featured Series
Recent Posts
-
ICFR and Why It Matters To Even Private Companies
At its core, ICFR is a comprehensive system of policies, procedures, and practices designed and maintained by a company’s management and personnel to provide reasonable assurance regarding the reliability of financial reporting…